

ACLs
The following page provides a management guide for ACLs (Access Control Lists). This document provides instructions on how to enable, disable, create, and delete ACLs for your WarpStream clusters.
Prerequisites
Section titled “Prerequisites”Before you begin, ensure you have administrative access to the WarpStream console and are familiar with the basic concepts of ACLs.
The current version of ACLs supports SASL and mTLS authentication method. Review Authentication for more information.
Important considerations
Section titled “Important considerations”There are a few things to keep in mind when using ACLs, which are covered below.
ACL Principal
Section titled “ACL Principal”ACLs operate using Principals, which are entities capable of being authenticated by the Authorizer. In the context of WarpStream agents, clients authenticate as a specific principal by using either SASL or mTLS authentication.
With SASL/PLAIN or SASL/SCRAM-SHA-512, the principal is identified by one of the three following:
- The assigned username (prefixed with
ccun_) - Chosen name during credential creation, (prefixed with
ccn_) - Chosen name during credential creation, without prefix
ccn_
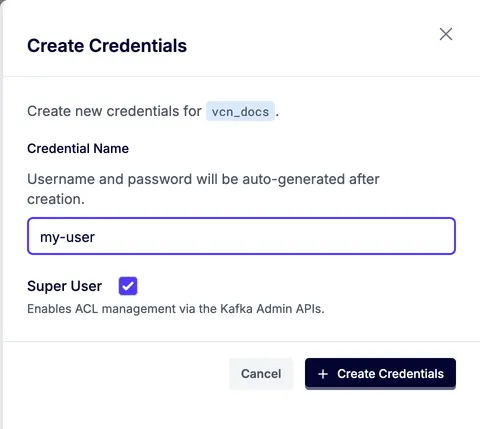
In the screenshot below, valid principal examples include: user_1234, ccn_user_1234, and ccun_3cc6c05a56b396fc084ef1e113150970cd148c87b5f64babfd3b8cf67d4d8840.
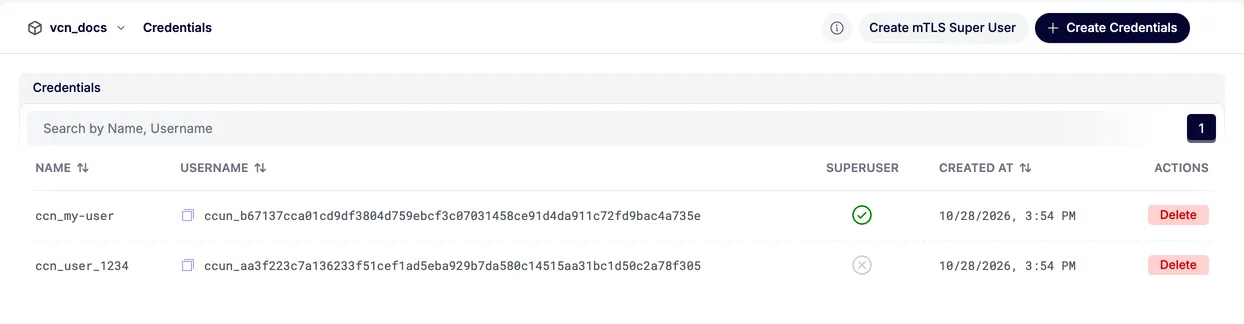
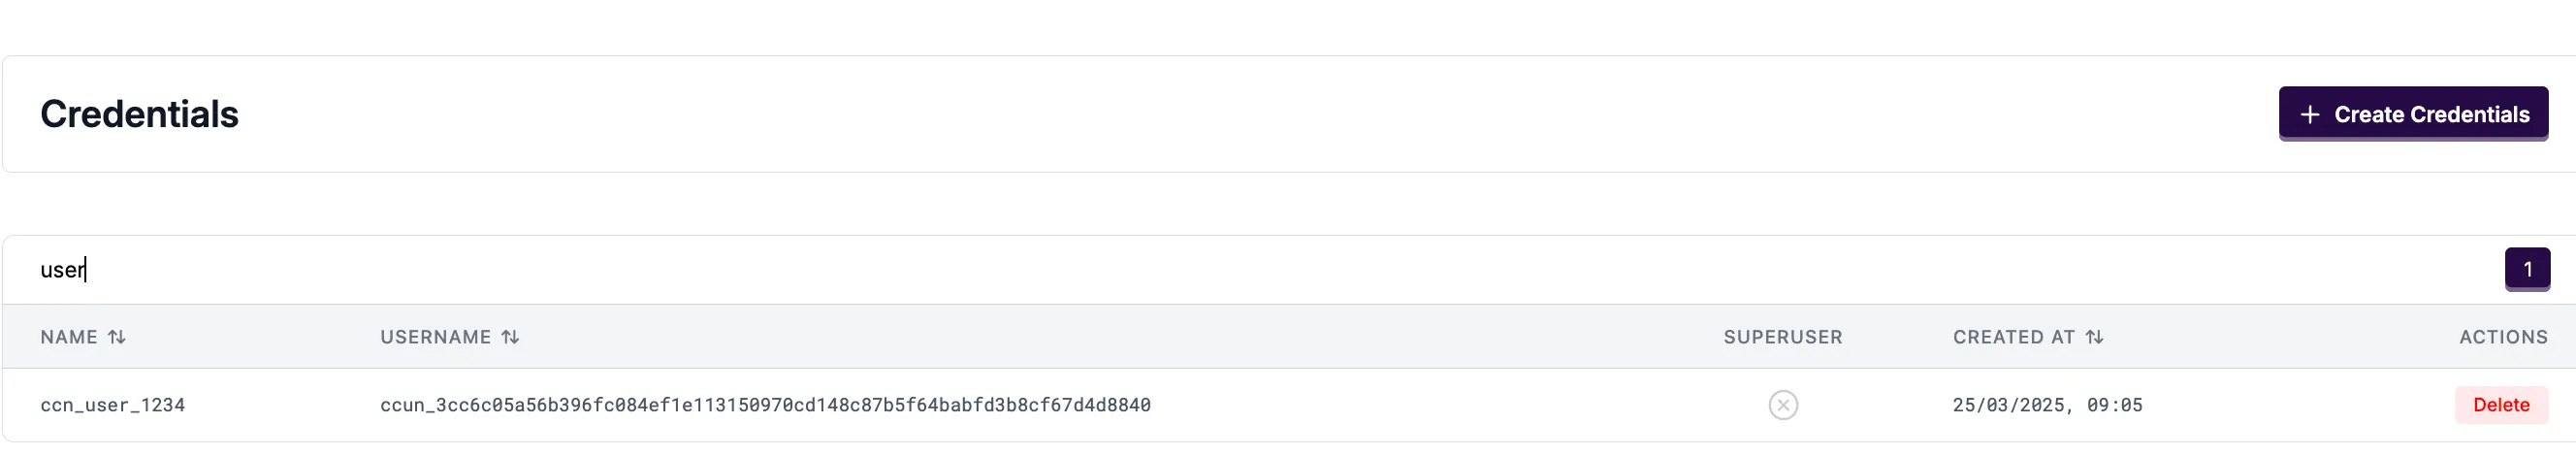
With mTLS, the principal is either the Distinguished Name(DN) from the client TLS certificate, or extracted from the DN according to the -tlsPrincipalMappingRule flag set in the Agents as described in the mutual tls authentication page.
With SASL/OAUTHBEARER the principal is identified by the subject of the OAuth token.
All principals should be prefixed with User: when creating ACL rules.
Super users
Section titled “Super users”In the context of ACLs, a ‘superuser’ is a specially designated user who possesses elevated privileges. Superusers are granted overarching access rights, allowing them to bypass standard ACL restrictions. This includes unrestricted abilities to create, modify, or delete resources, and to manage access controls for other users.
For SASL/PLAIN or SASL/SCRAM-SHA-512, you can authorize as super user by setting your SASL username as either the generated cluster credentials username(ccun_) or by using the “Name” which you set while generating credentials. You can create super users through the credentials, as explained at SASL Generating Credentials.
For mTLS, you can create super users by clicking the “Create mTLS Super User” button in the Credentials page and entering the certificate DN or TLS principal.
For SASL/OAUTHBEARER, you can create super users by clicking the “Create mTLS Super User” button in the Credentials page and entering the OAuth subject you want to be a super user.
Caching of ACLs
Section titled “Caching of ACLs”For performance reasons, ACLs are cached, so changes to ACLs may take between 30 seconds to 1 minute to take effect. Plan accordingly when updating ACLs in a production environment to ensure a smooth transition.
allow.everyone.if.no.acl.found
Section titled “allow.everyone.if.no.acl.found”Warpstream does not implement the allow.everyone.if.no.acl.found Kafka configuration, because:
- It’s not safe for production environments.
- You can get the equivalent (and safer) behaviour by simply using Super users, who are authorized to access everything.
ACL Shadowing
Section titled “ACL Shadowing”ACL Shadowing allows a WarpStream cluster to evaluate Kafka ACLs against live traffic without enforcing authorization decisions. This mode is designed to help operators validate ACL behavior before enabling full ACL enforcement.
When ACL Shadowing is enabled:
- All incoming requests are evaluated against the cluster’s configured ACLs.
- Authorization results are not enforced (no requests are blocked).
- Would-be denials are logged and surfaced through Diagnostics.
ACL Shadowing can be enabled from the WarpStream Console in the ACLs tab for your cluster or via Terraform.
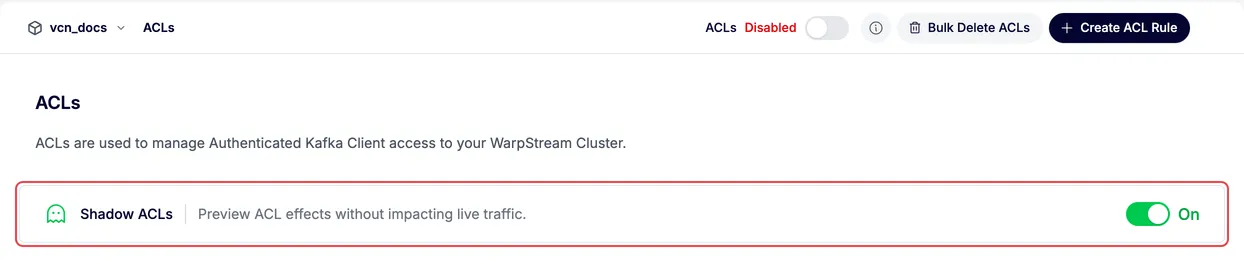
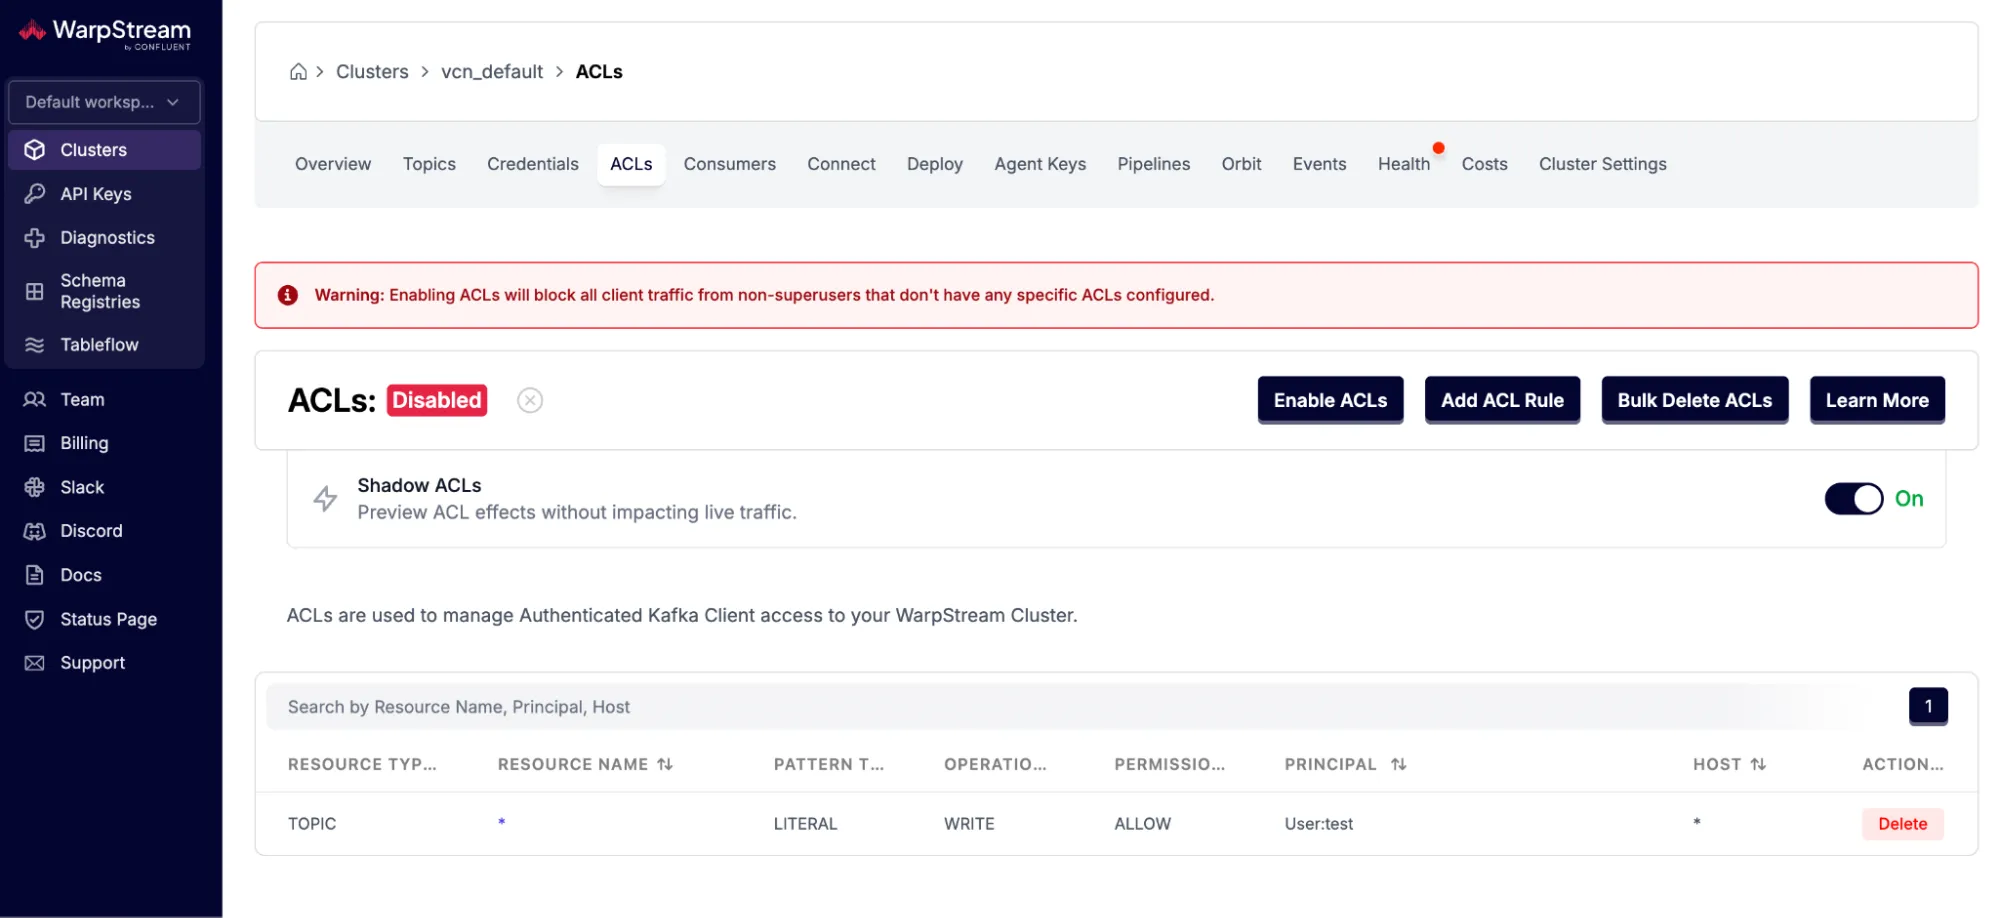
Note that ACL Shadowing will be automatically disabled when you enable ACLs for your cluster.
Enabling and Disabling ACLs
Section titled “Enabling and Disabling ACLs”To Enable ACLs
Section titled “To Enable ACLs”- Navigate to the WarpStream console.
- Select the desired Virtual Cluster, for example
vcn_default. - Click on the
ACLstab. - You will see the
ACLs: Disabledstatus label if ACLs are currently disabled.
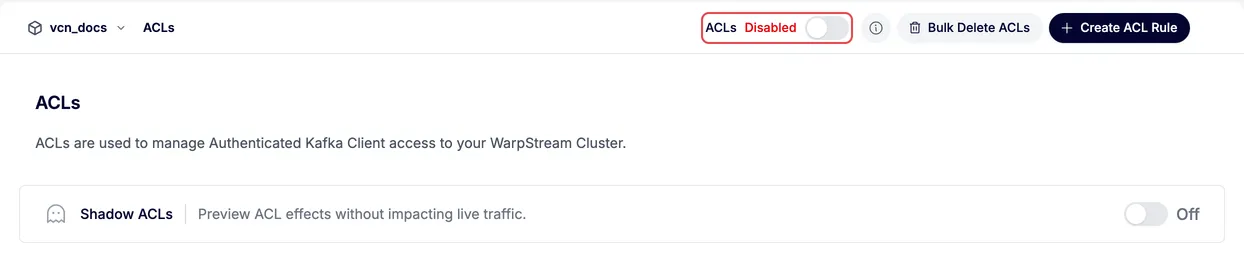
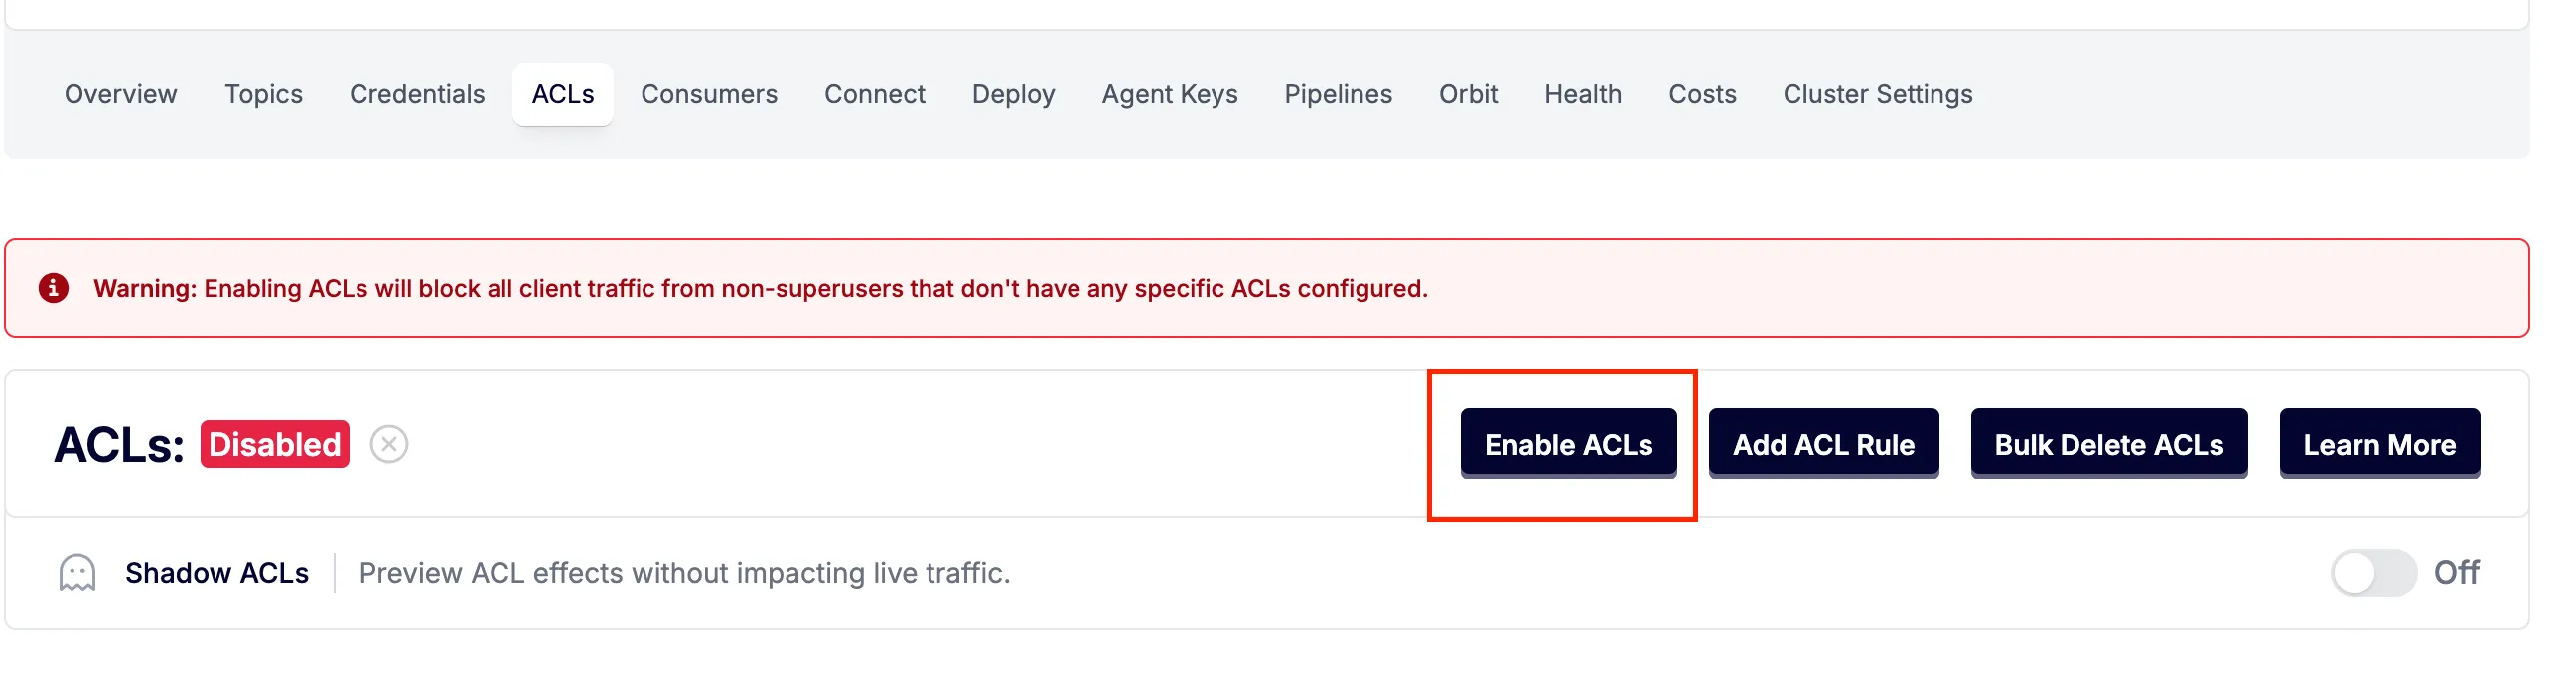
- Click on the
Enable ACLsbutton to change its status toEnabled.
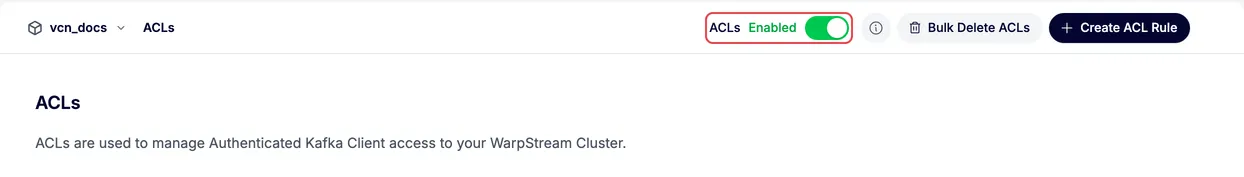
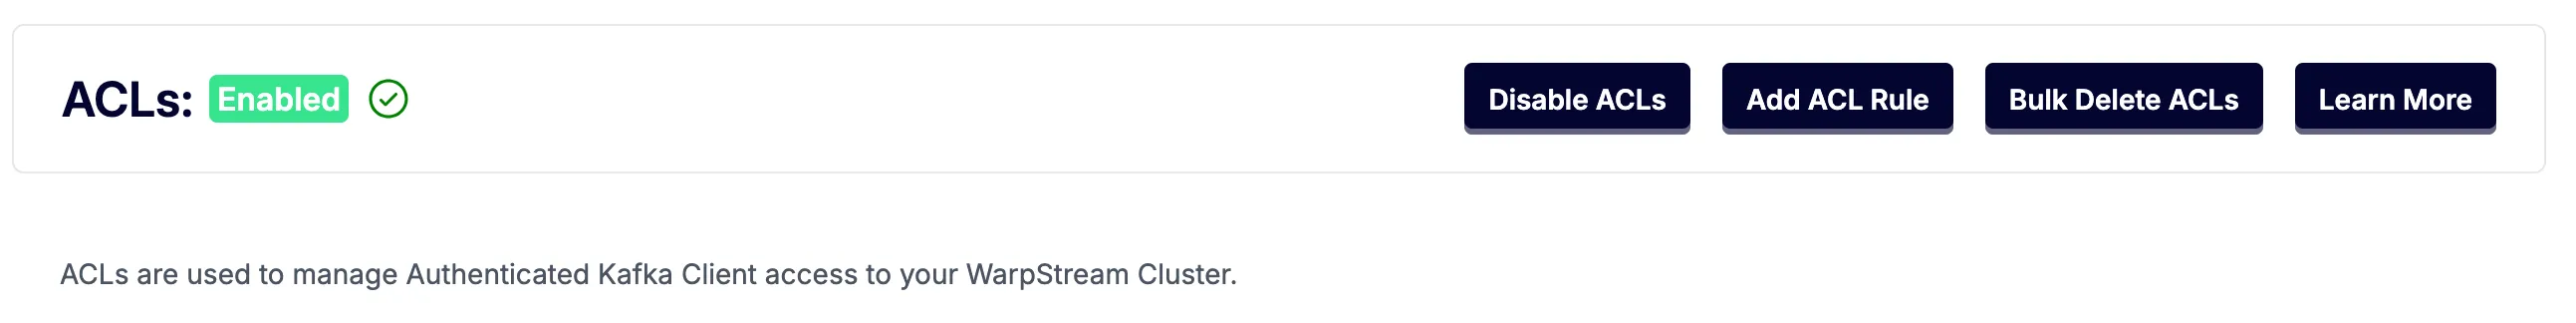
To Disable ACLs
Section titled “To Disable ACLs”- Follow the same steps to navigate to the
ACLstab of your Virtual Cluster. - If ACLs are enabled, you will see the
ACLs: Enabledstatus label. - Click on the
Disable ACLsbutton to turn off ACLs for the cluster.
Enable/Disable Using the HTTP API
Section titled “Enable/Disable Using the HTTP API”Alternatively, you can switch ACLs on and off using the HTTP APIs, which is a convenient alternative to doing it through the console UI. Refer to DescribeConfiguration and UpdateConfiguration for details.
Generating Credentials
Section titled “Generating Credentials”To interact with WarpsSream clusters, you need to generate credentials:
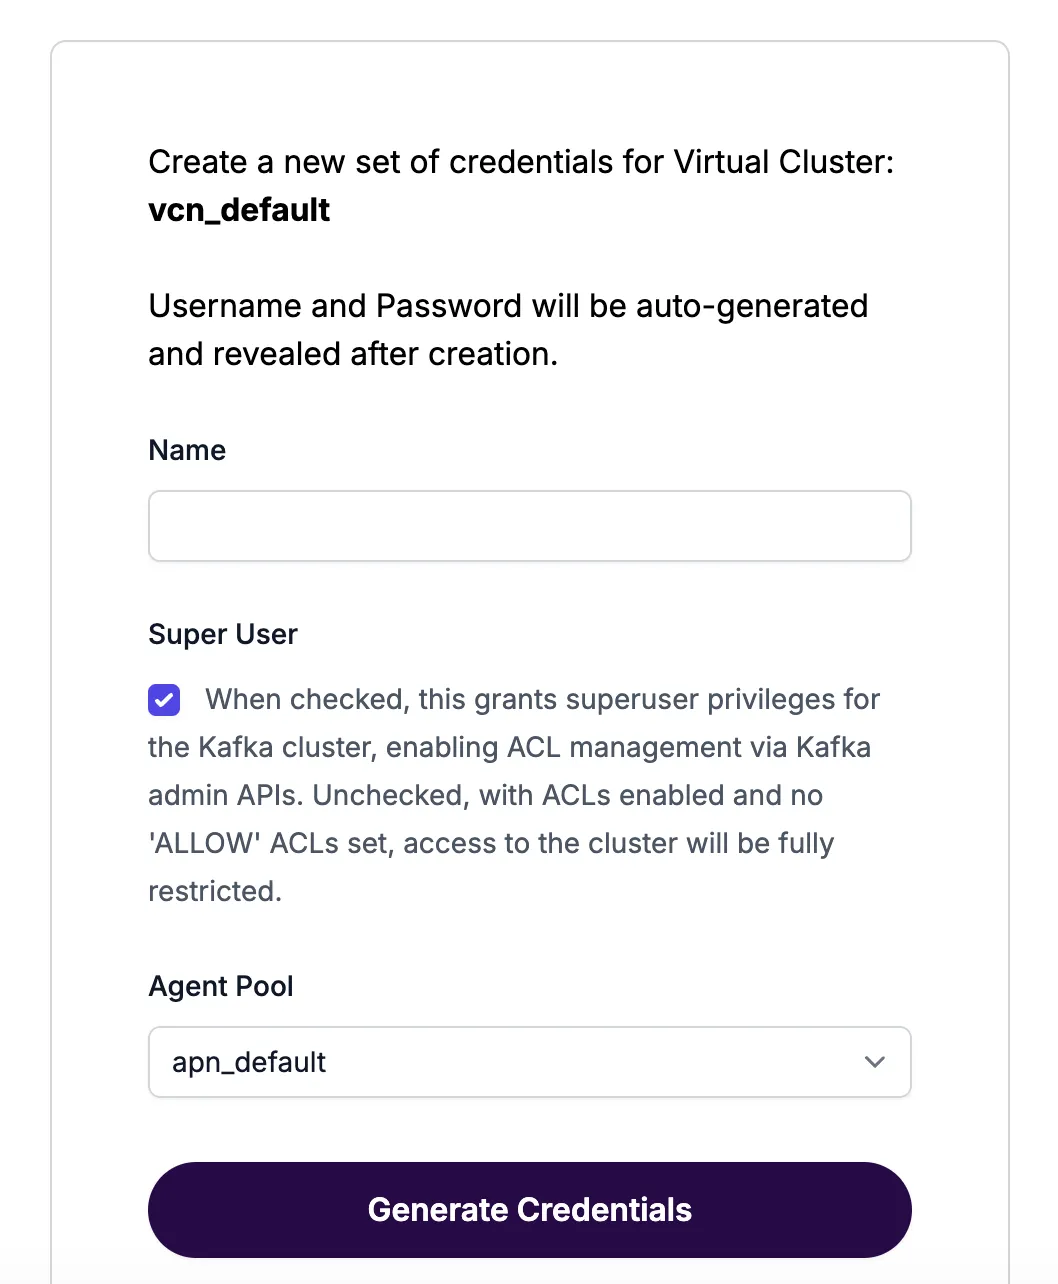
- Within the WarpStream console, navigate to the
Credentialstab of your Virtual Cluster. - Click on
Generate Credentials. - Provide a name for the credentials.
- If necessary, enable
Super Userfor broader permissions.- Important: If a resource has no associated ACLs, then only superusers can access that resource.
- Click
Generate Credentials. The credentials will be displayed for you to use with the CLI.
Managing ACLs via WarpStream Console
Section titled “Managing ACLs via WarpStream Console”- Navigate to the WarpStream console.
- Select the desired Virtual Cluster, for example
vcn_default. - Click on the
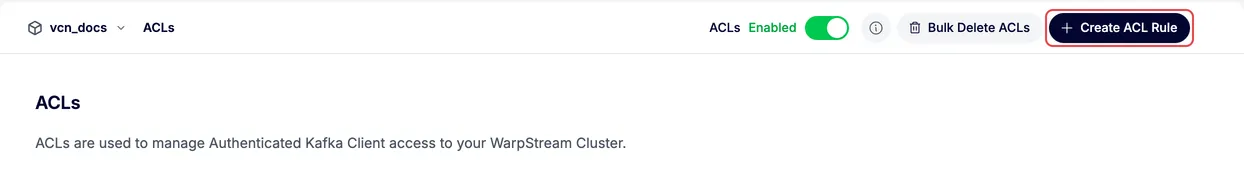
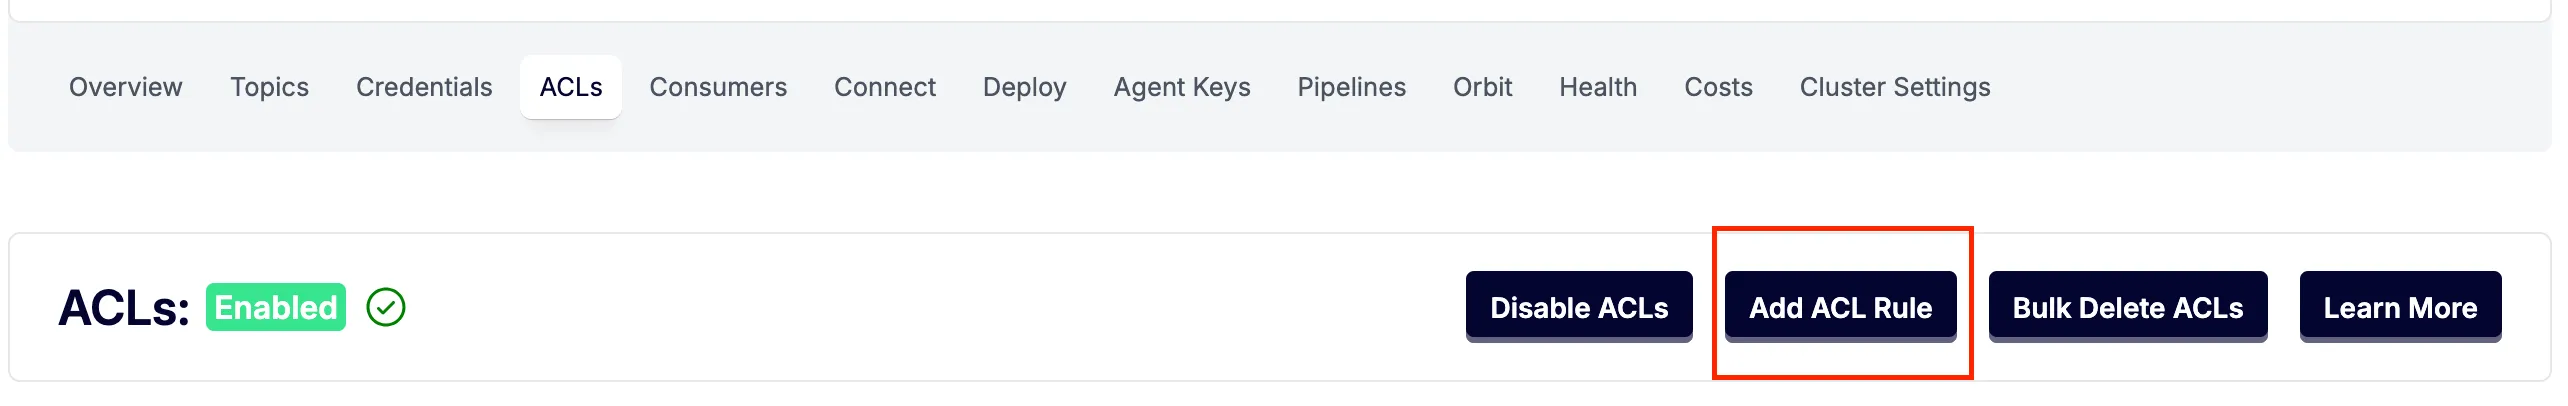
ACLstab. - Click “Add ACL Rule”
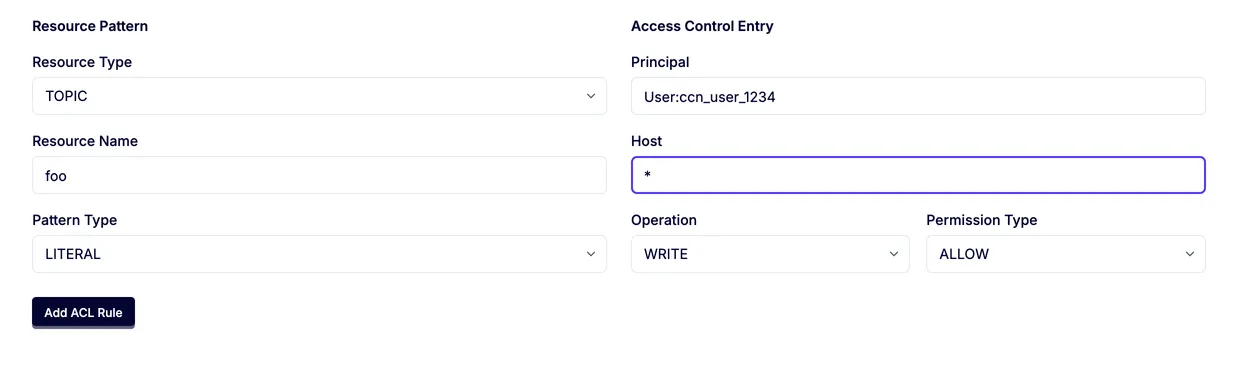
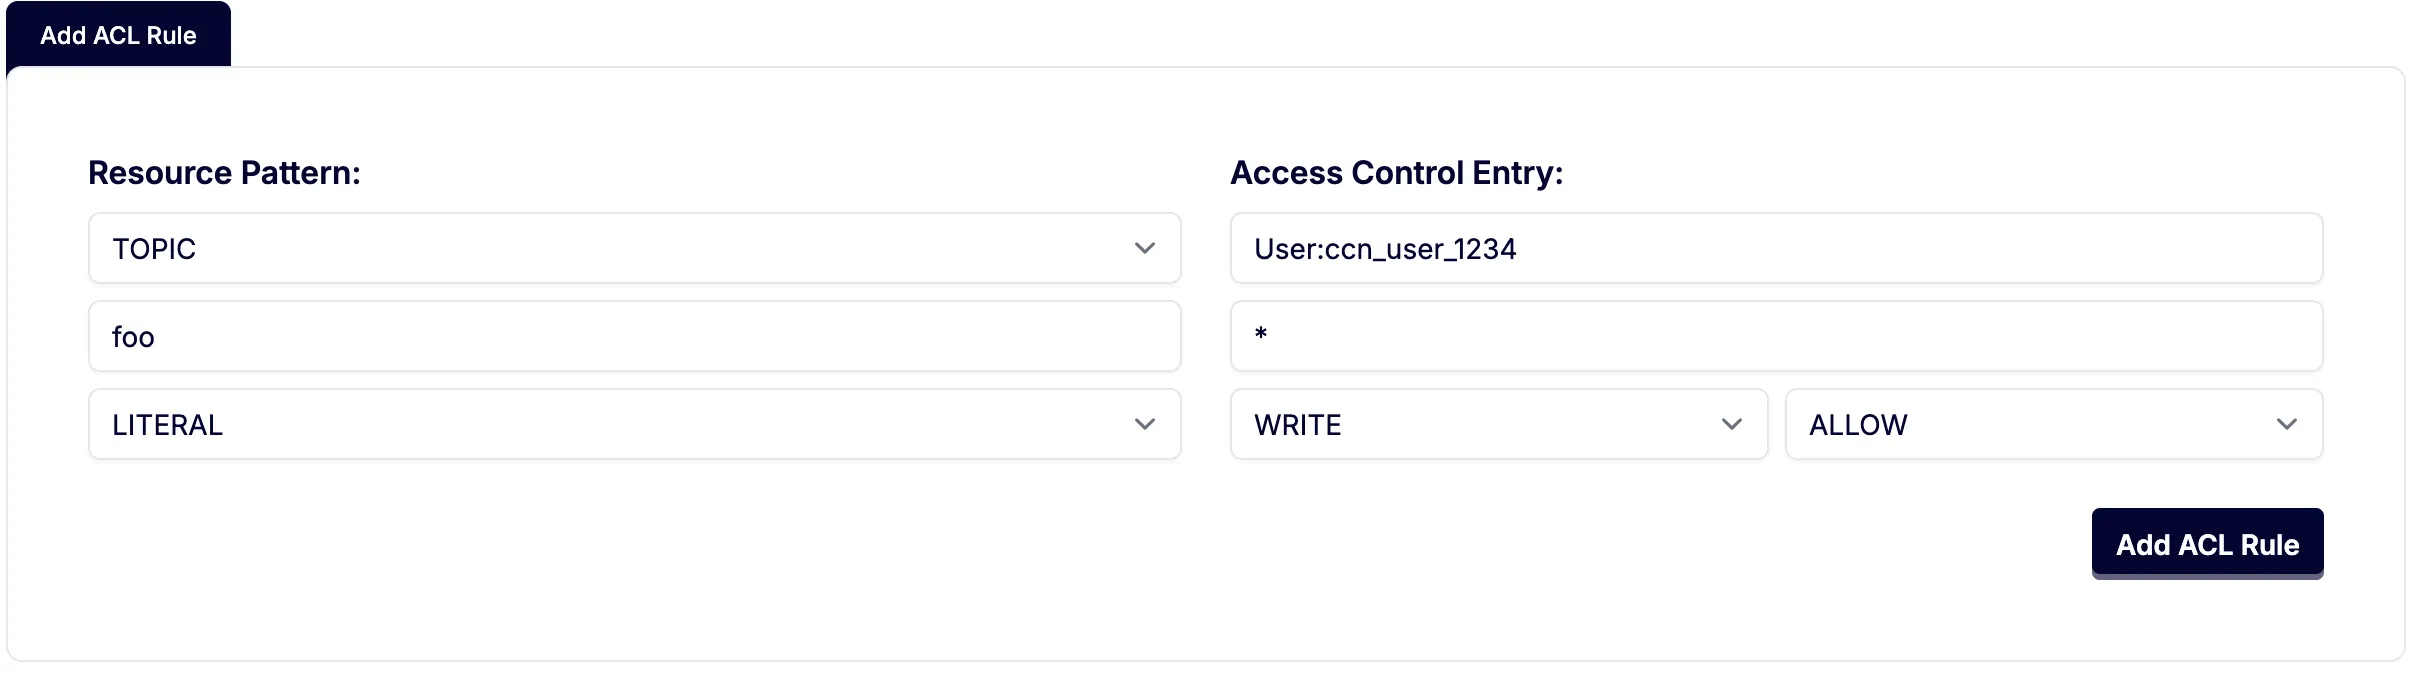
- Fill in the rule information. In this example we are creating a
TOPICACL for topics that match the namefooexactly for the Userccn_user_1234and allowing that user toWRITEto the topic.
For information on ACL resource types and operations see the Confluent Operation Documentation.
Managing ACLs via Kafka API
Section titled “Managing ACLs via Kafka API”To manage ACLs via the Kafka API, use the Kafka Admin API with appropriate Kafka credentials.
Managing ACLs via HTTP API
Section titled “Managing ACLs via HTTP API”You can create, list, and delete ACLs using the WarpStream HTTP API. See the ACLs API Reference for full endpoint documentation.
Managing ACLs via Terraform
Section titled “Managing ACLs via Terraform”ACLs can be managed using the WarpStream Terraform provider.
Create an ACL
Section titled “Create an ACL”To create an ACL, use the createAcls method with the required ACL details:
_, err = admin.CreateACLs(  context.Background(),  kafka.ACLBindings{{    Type:                kafka.ResourceTopic,    Name:                "topic_name",    ResourcePatternType: kafka.ResourcePatternTypeLiteral,
    // See above the above ACL Principal section for information.    Principal:           "User:<credential_principal>",
    Host:                "*", // Request can come from any host.    Operation:           kafka.ACLOperationWrite,    PermissionType:      kafka.ACLPermissionTypeAllow,  }},)if err != nil {  fmt.Printf("Failed to create ACLs: %s\n", err.Error())  os.Exit(1)}
Delete an ACL
Section titled “Delete an ACL”To delete an ACL, use the deleteAcls method with a filter matching the ACL you wish to remove:
_, err = admin.DeleteACLs(  context.Background(),  kafka.ACLBindingFilters{{    Type:                kafka.ResourceTopic,    Name:                "topic_name",    ResourcePatternType: kafka.ResourcePatternTypeLiteral,
    // See above the above ACL Principal section for information.    Principal:           "User:<credential_username>",
    Host:                "*",    Operation:           kafka.ACLOperationWrite,    PermissionType:      kafka.ACLPermissionTypeAllow,  }},)if err != nil {  fmt.Printf("Failed to delete ACLs: %s\n", err)  os.Exit(1)}
The examples above use the librdkafka package from Go. You can also try the bin/kafka-acls.sh script from Apache Kafka®’s official binary release for more hands-on experience:
bin/kafka-acls.sh --bootstrap-server localhost:9092 --remove --allow-principal User:<credential_username> --allow-principal User:Alice --allow-host 198.51.100.0 --allow-host 198.51.100.1 --operation Read --operation Write --topic Test-topicbin/kafka-acls.sh --bootstrap-server localhost:9092 --add --allow-principal User:Bob --allow-principal User:<credential_username> --allow-host 198.51.100.0 --allow-host 198.51.100.1 --operation Read --operation Write --topic Test-topicUsing the ANY Resource Type in ACLs
Section titled “Using the ANY Resource Type in ACLs”Our system supports creating ACLs with the resource type ANY through the console, API, and Terraform. This differs from standard Apache Kafka, where clients typically cannot create ACLs with resource type ANY and may reject them.
Denied Authorization Logs
Section titled “Denied Authorization Logs”Logs for denied authorizations are enabled by default and can be enable/disabled by setting the -enableACLLogs flag or WARPSTREAM_ENABLE_ACL_LOGS environment variable to true or false on the Agents.
Any actions that are denied due to a missing ACL or an explicit DENY ACL will show up in these logs. An example log is below:
{"time":"2025-03-13T13:02:05.176353-05:00","level":"WARN","msg":"ACL Denied Operation on resource","principal":"User:ccun_9c5d...","operation":"CREATE","host":"127.0.0.1:56216","resource_type":"TOPIC","resource_name":"foo"}In the example above we can see the user User:ccun_9c5d... tried to CREATE a TOPIC called foo and was denied.